From mandate to measurable progress.
Whether you report to OMB, a board or an authorizing official, ZTASphere turns zero trust from a slide into a score backed by evidence.
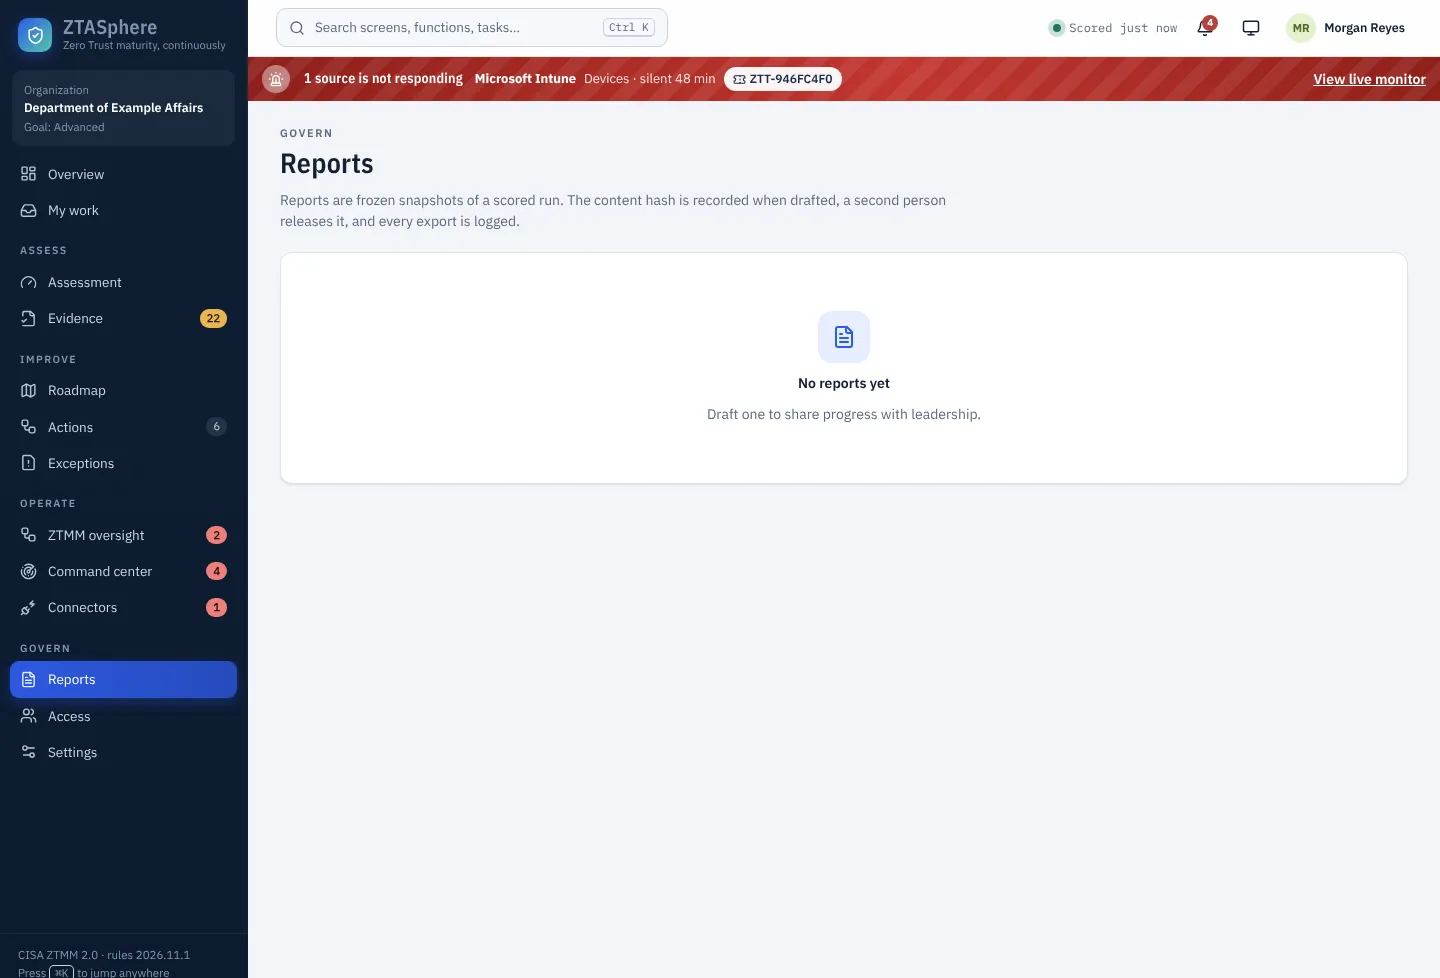
Show progress against EO 14028 and OMB M-22-09.
Agencies are required to show measurable progress toward zero trust, and CISA ZTMM 2.0 is the yardstick most of them and their auditors use. ZTASphere maps each strategy goal to ZTMM functions and collects the evidence automatically.
- CDM-aligned reporting alongside executive, pillar and gap reports
- OMB M-26-14 logging evidence: source inventory, coverage and feed health
- OMB M-26-15 post-quantum inventory and encryption scoring
- Deploys in AWS GovCloud, Azure Government or fully air-gapped
- Classification banner configurable per deployment
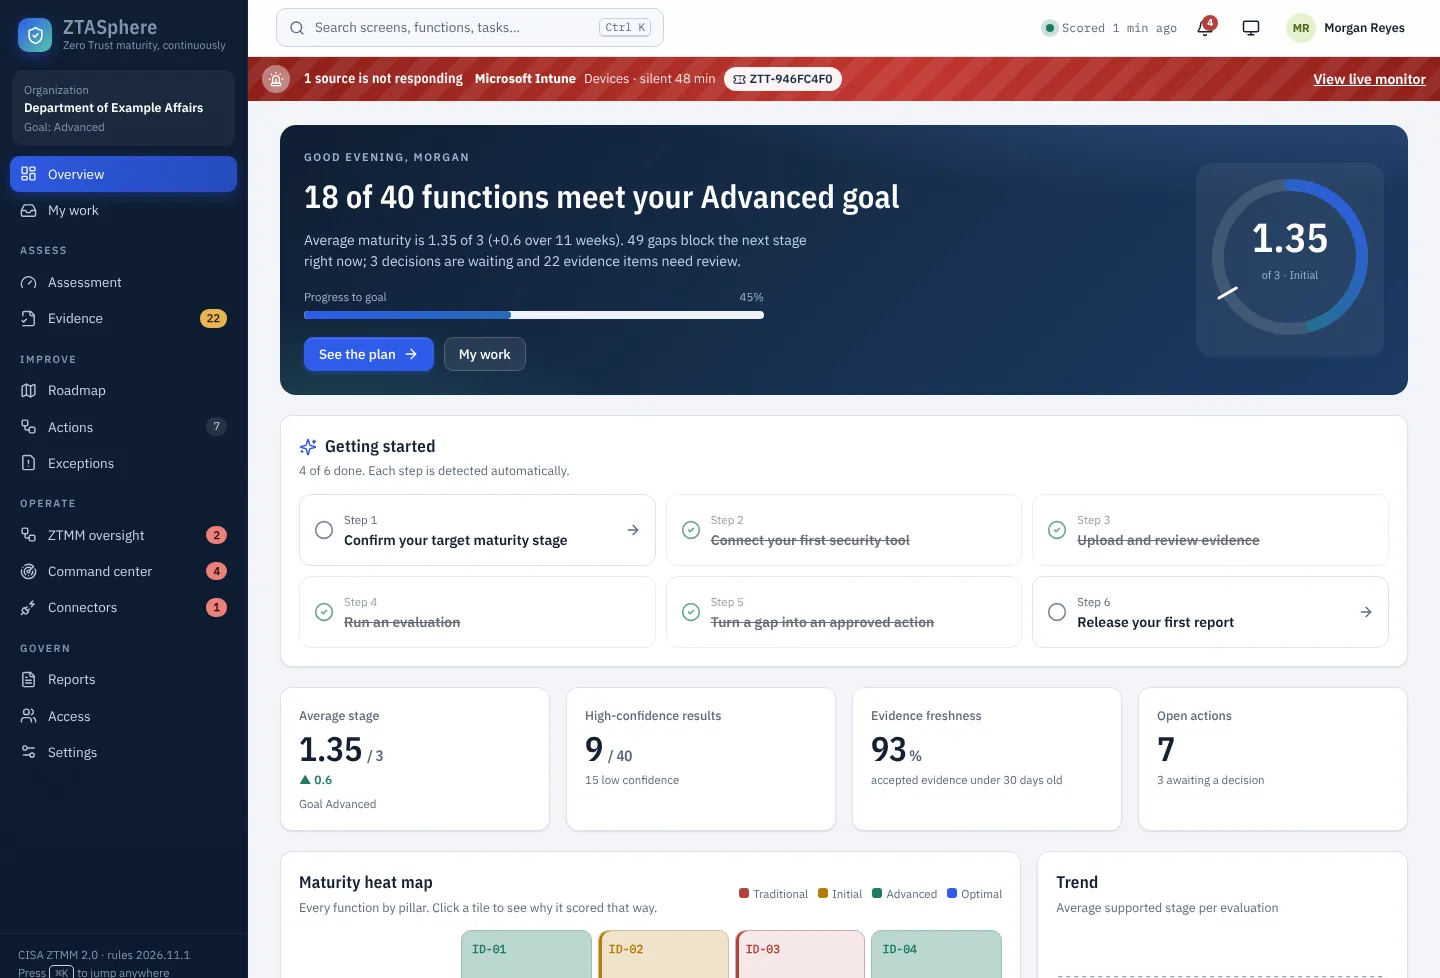
One maturity language across every business unit.
Financial services, healthcare, energy and defense suppliers are adopting the CISA model and NIST SP 800-207 as their zero trust reference. ZTASphere gives the board a single, comparable score and gives each business unit its own roadmap.
- Multi-cloud evidence from Prisma Cloud, Amazon Bedrock and more
- Target stage per organization so goals match risk appetite
- Tool rationalization: see which tools actually prove which functions
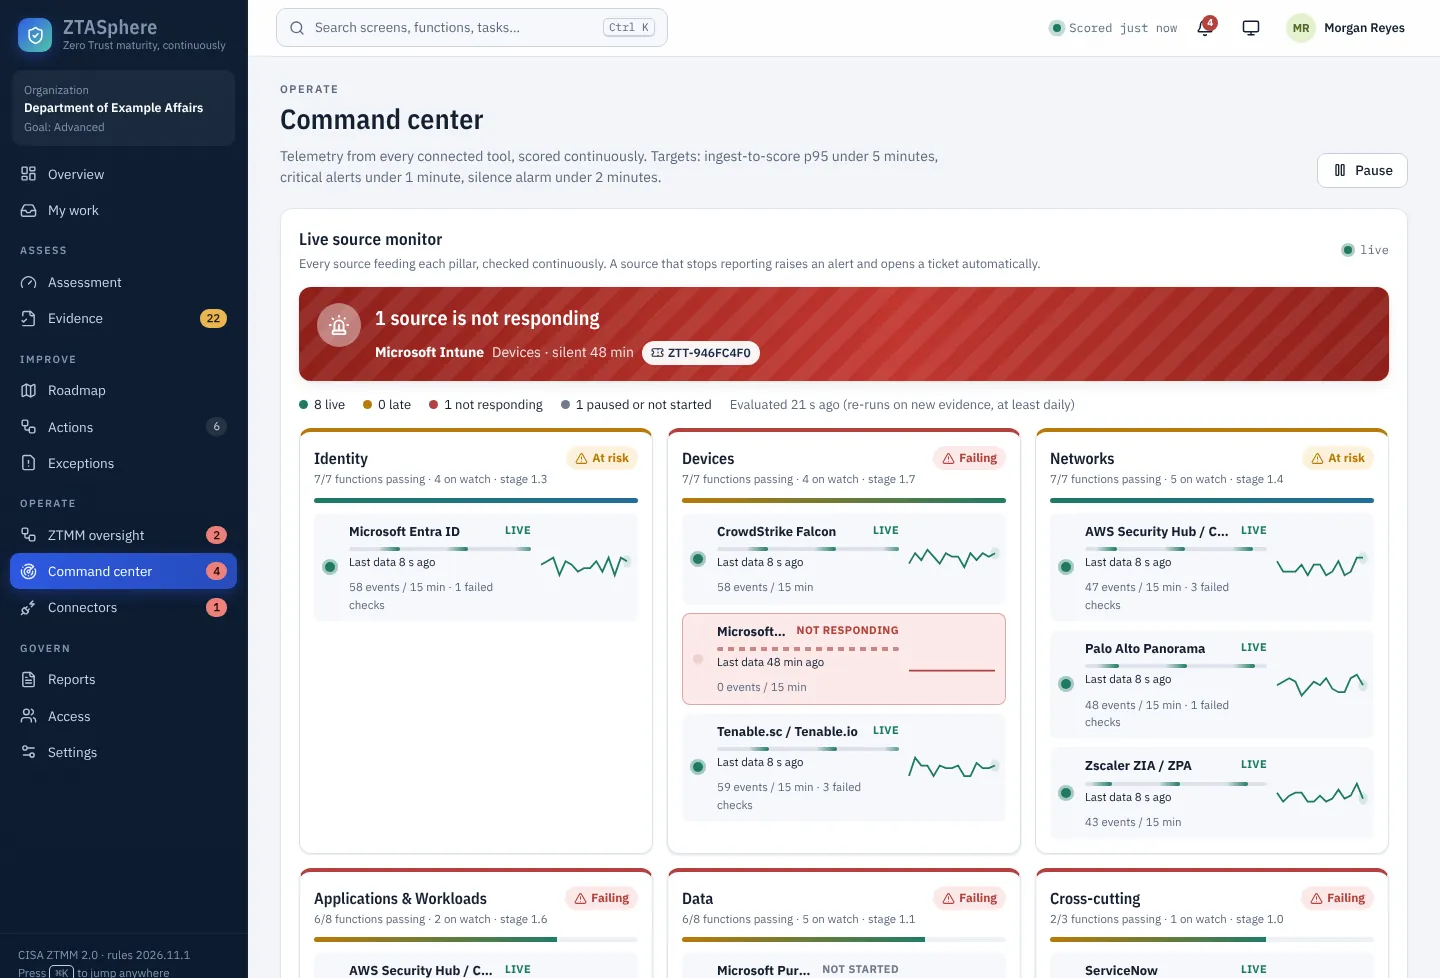
Continuous compliance becomes an operational signal.
The SOC sees zero trust posture next to the alerts it already handles. A silent feed or a dropped maturity level becomes a ticket with an owner, not a finding six months later.
- Feed health with live, late, down and blocked states and escalation
- Ticketing outbox to ServiceNow, Jira or signed webhooks
- Wall display for the ZTMM oversight view
- SOC analyst role that can acknowledge alerts and nothing more
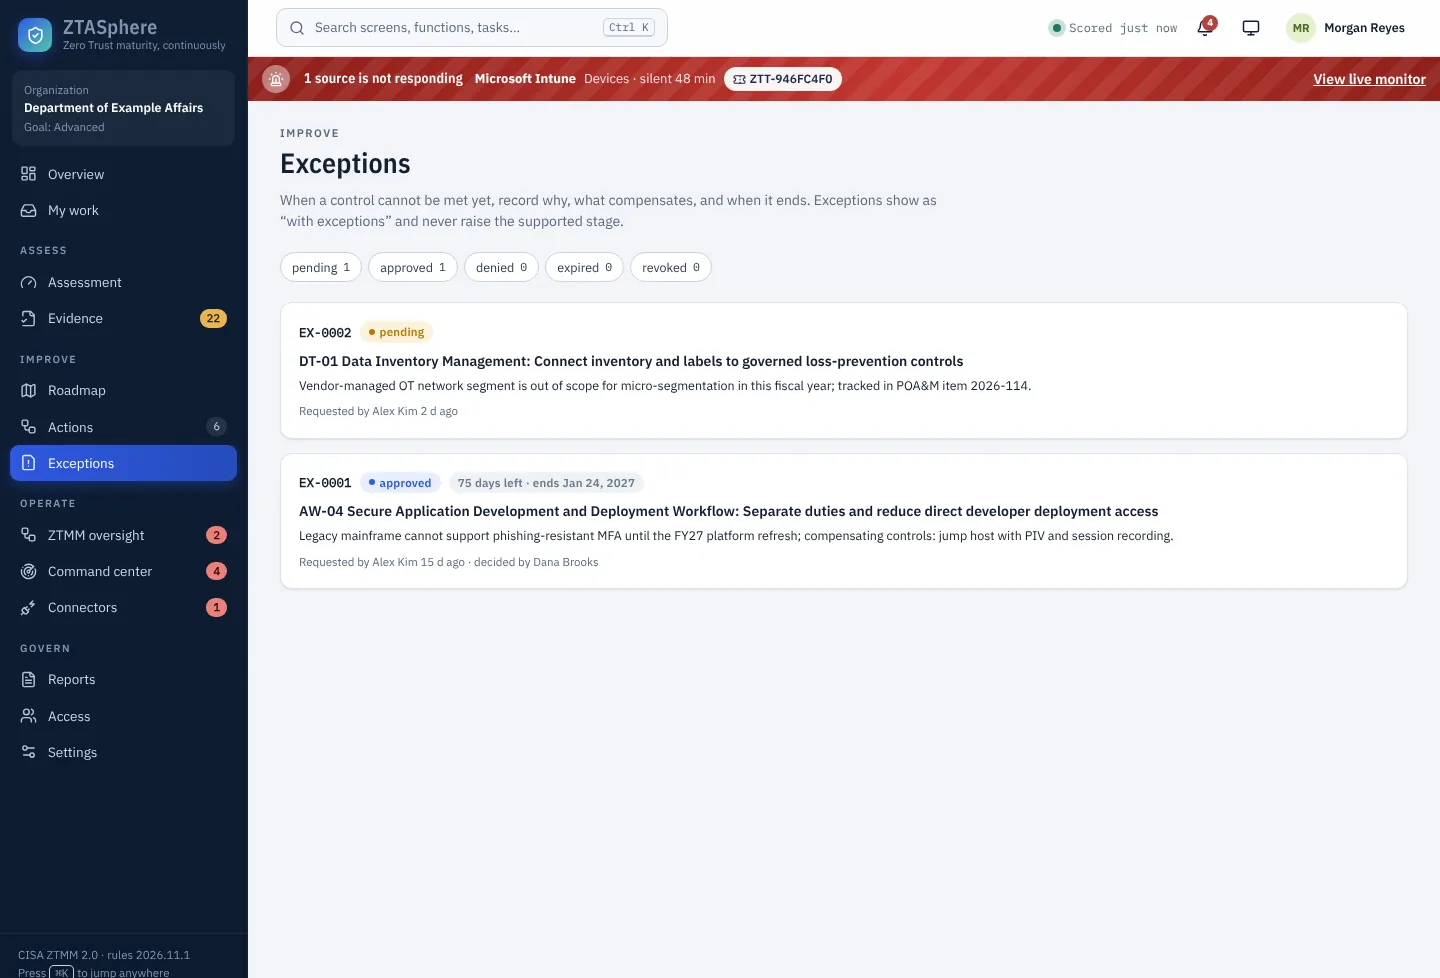
Evidence packages that stand up to review.
Assessors get read-only access to every score, the evidence behind it and the history of every decision. The audit log is hash-chained, so a single click confirms no record was altered or removed.
- Read-only auditor role with chain verification
- Risk approver role for actions, exceptions and report release
- Exportable reports released through a draft and approval step
Seventeen roles, so everyone sees exactly their part.
Permissions follow least privilege and separation of duties. A few of them:
Executive viewer
Reads results and reports. Changes nothing.
Assessor
Runs evaluations and integrations, requests evidence, drafts reports.
Pillar owner
Submits evidence and actions, requests exceptions for their pillar.
Independent reviewer
Reviews evidence submitted by others.
Risk approver (AO)
Approves actions and exceptions, releases reports, approves baselines.
Read-only auditor
Reads and verifies the audit chain.
SOC analyst
Acknowledges alerts from the live monitor.
Connector operator
Manages connectors and their health.
See your zero trust maturity, scored on live evidence.
Bring one pillar or all five. In a working session we connect to the tools you already run and show what ZTASphere sees, using your own environment's language and priorities.