Prove zero trust maturity. Every day, not every audit.
ZTASphere reads evidence from the security tools you already own, scores all 40 functions and 182 criteria of the CISA Zero Trust Maturity Model, and keeps that score current. Leaders see where they stand. Owners see what to fix next.
Illustrative animation. Pillar stages are sample values.
You already bought the tools. What you can't show is the proof.
Most organizations still measure zero trust maturity by hand, once or twice a year, from screenshots and spreadsheets collected from dozens of tool owners. The result is out of date on the day it is published.
Point-in-time and argued
- About 9,000 staff hours a year spent gathering and re-gathering evidence (business case estimate)
- Scores that depend on who filled in the spreadsheet
- No warning when a control quietly drifts or a feed goes dark
- Roadmaps disconnected from the gaps that matter most
Continuous and defensible
- Evidence collected automatically from 17 security tools, read-only
- Scored only on accepted, current evidence; anything older than 30 days stops counting
- Alerts the SOC when a source goes silent or a maturity level drops
- Gap-to-goal roadmap with approvals and verification built in
One closed loop from tool telemetry to verified improvement.
Connect
Link the identity, endpoint, network, cloud and data tools you already run.
Understand
Map every signal to the ZTMM function and criterion it proves.
Assess
Score 40 functions from fresh, accepted evidence only.
Plan
Rank the gaps between today and your target stage.
Act
Run improvement actions with approval and a canary step.
Verify
An independent reviewer confirms the result with new evidence.
Monitor
Watch every feed and every level, and alert on drift.
Built for the people who answer for zero trust.
Real screens from ZTASphere, shown with the built-in demo organization.
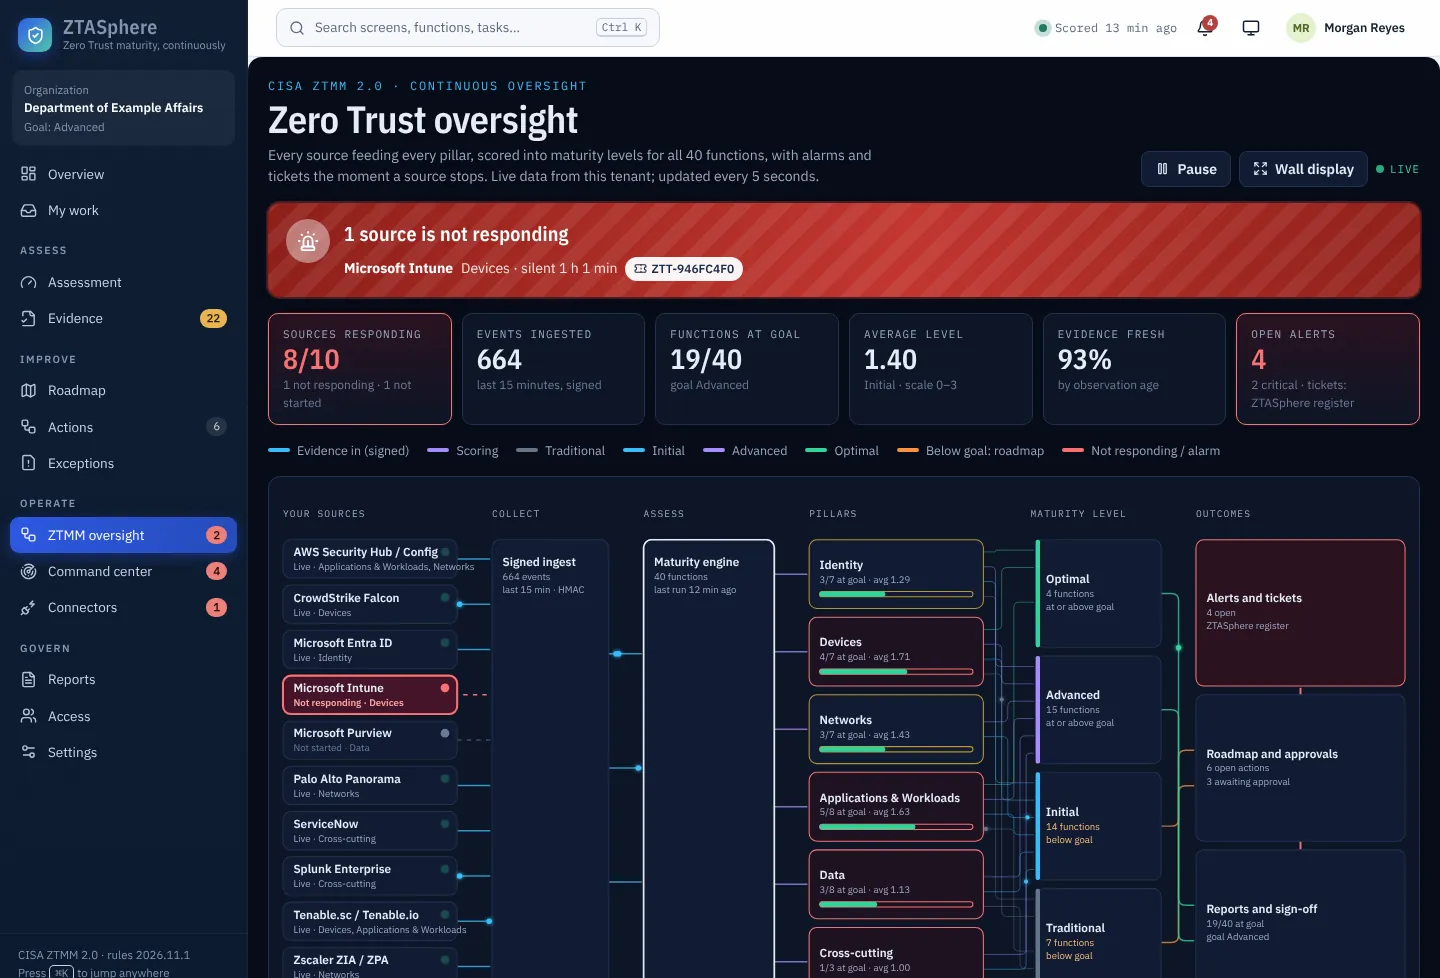
See every source, pillar and level at once.
An animated map from each connected tool to the pillar it informs and the ZTMM stage it supports. Silent sources raise an alarm and a ticket automatically. Put it on the SOC wall display.
- Pillar × stage matrix and 40 function tiles
- Feed health: live, late, down, blocked
- Open alerts linked to tickets
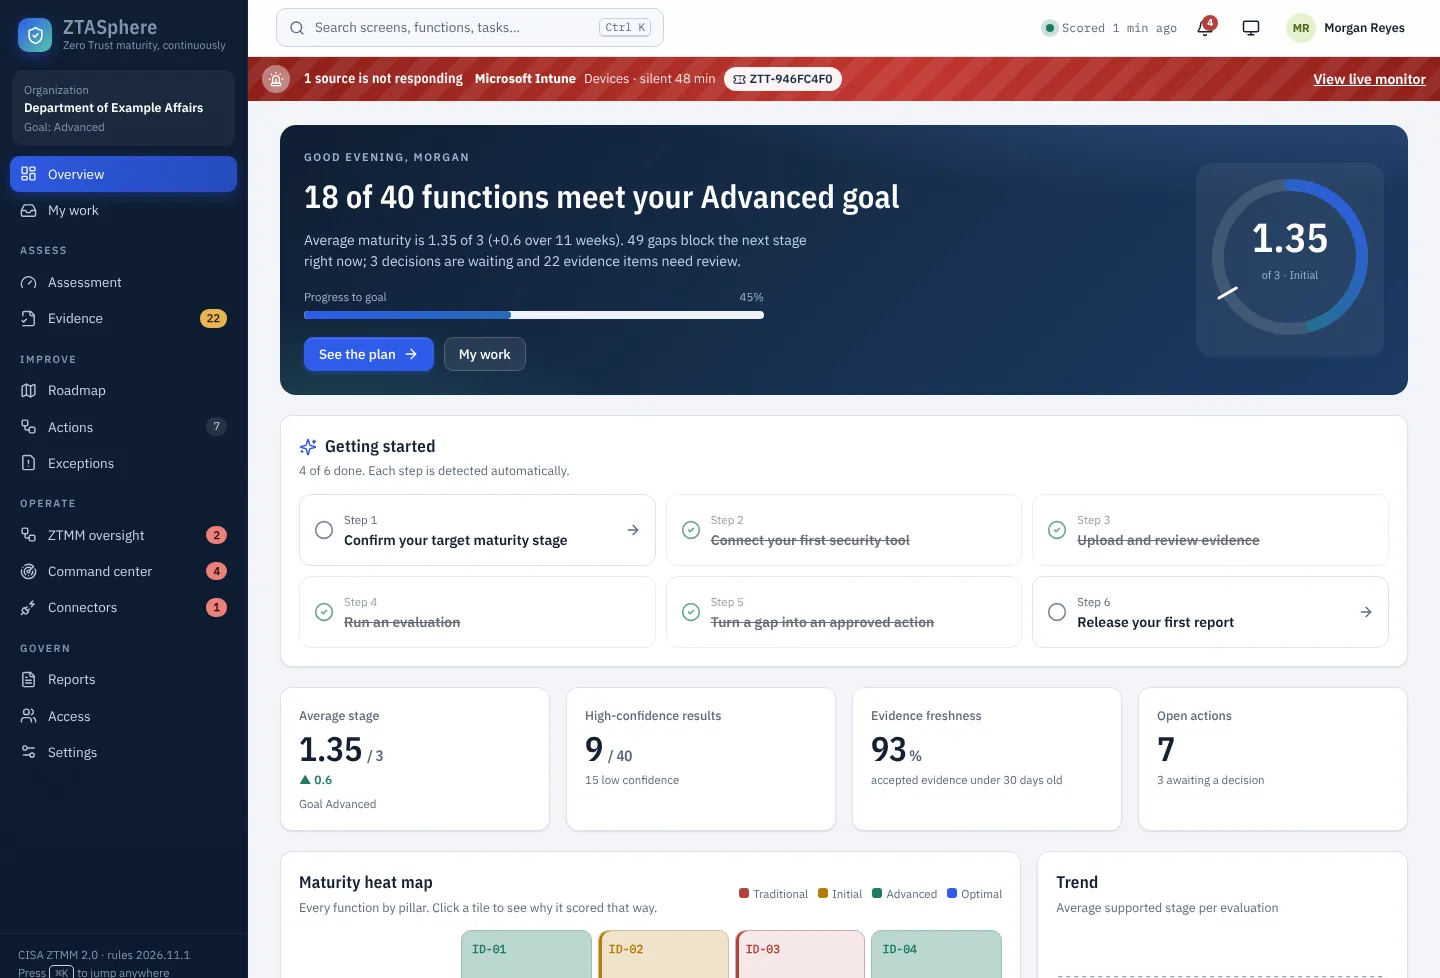
The answer leadership asks for, in one sentence.
"18 of 40 functions meet your Advanced goal." The overview tells executives where they stand against the target stage, what changed, and what is waiting on a decision.
- Average stage across all functions
- High-confidence results and evidence freshness
- Maturity heat map and trend
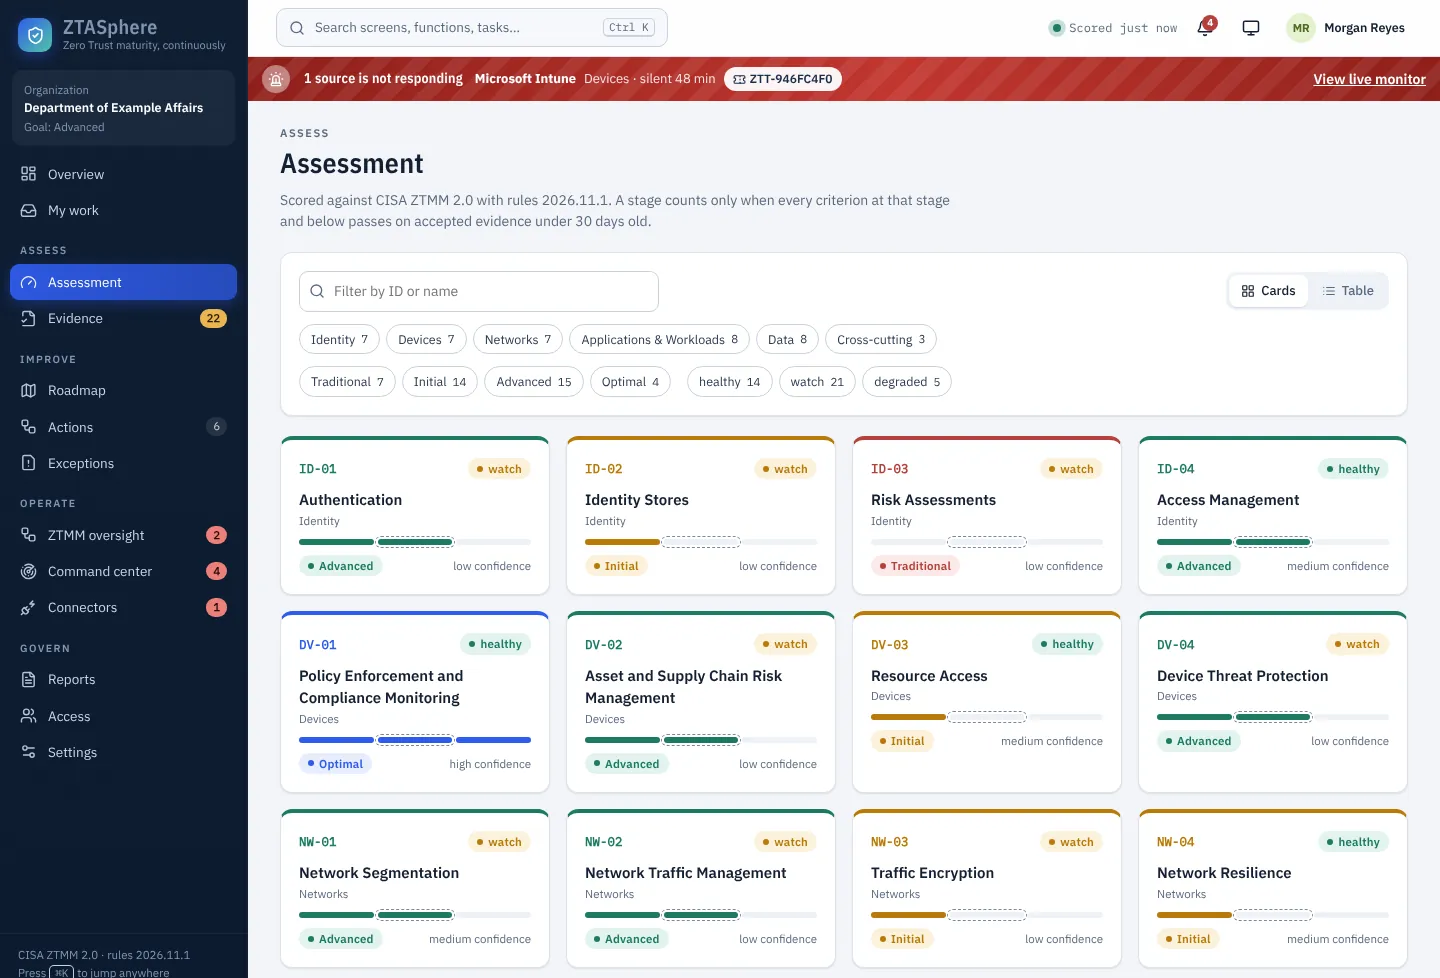
Every function, every criterion, traced to evidence.
A stage counts only when every one of its criteria is met by accepted evidence observed in the last 30 days. Drill from a pillar to a function, to the criterion, to the exact file or API record behind it.
- Confidence shown next to every score
- Filter by pillar, stage, health
- Versioned rules for repeatable results
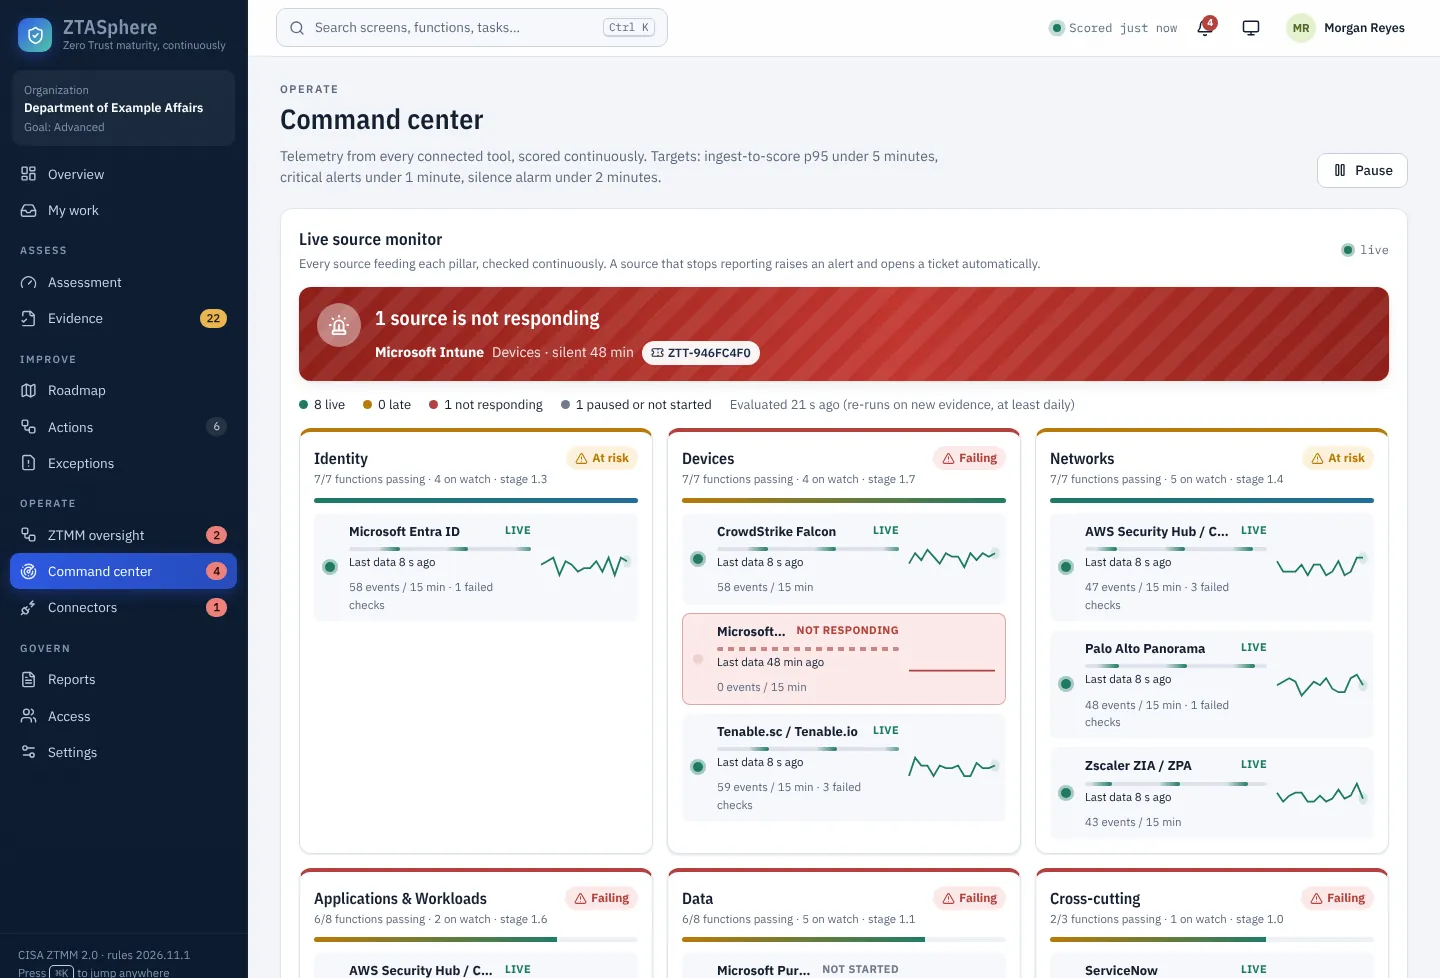
Know the moment your evidence goes dark.
The command center watches every connected source. When a feed is late or down, ZTASphere escalates, opens a ticket, and resolves it automatically when data returns.
- Per-pillar connector health and sparklines
- Tickets to ServiceNow, Jira or a signed webhook
- Target: ingest-to-score in under 5 minutes
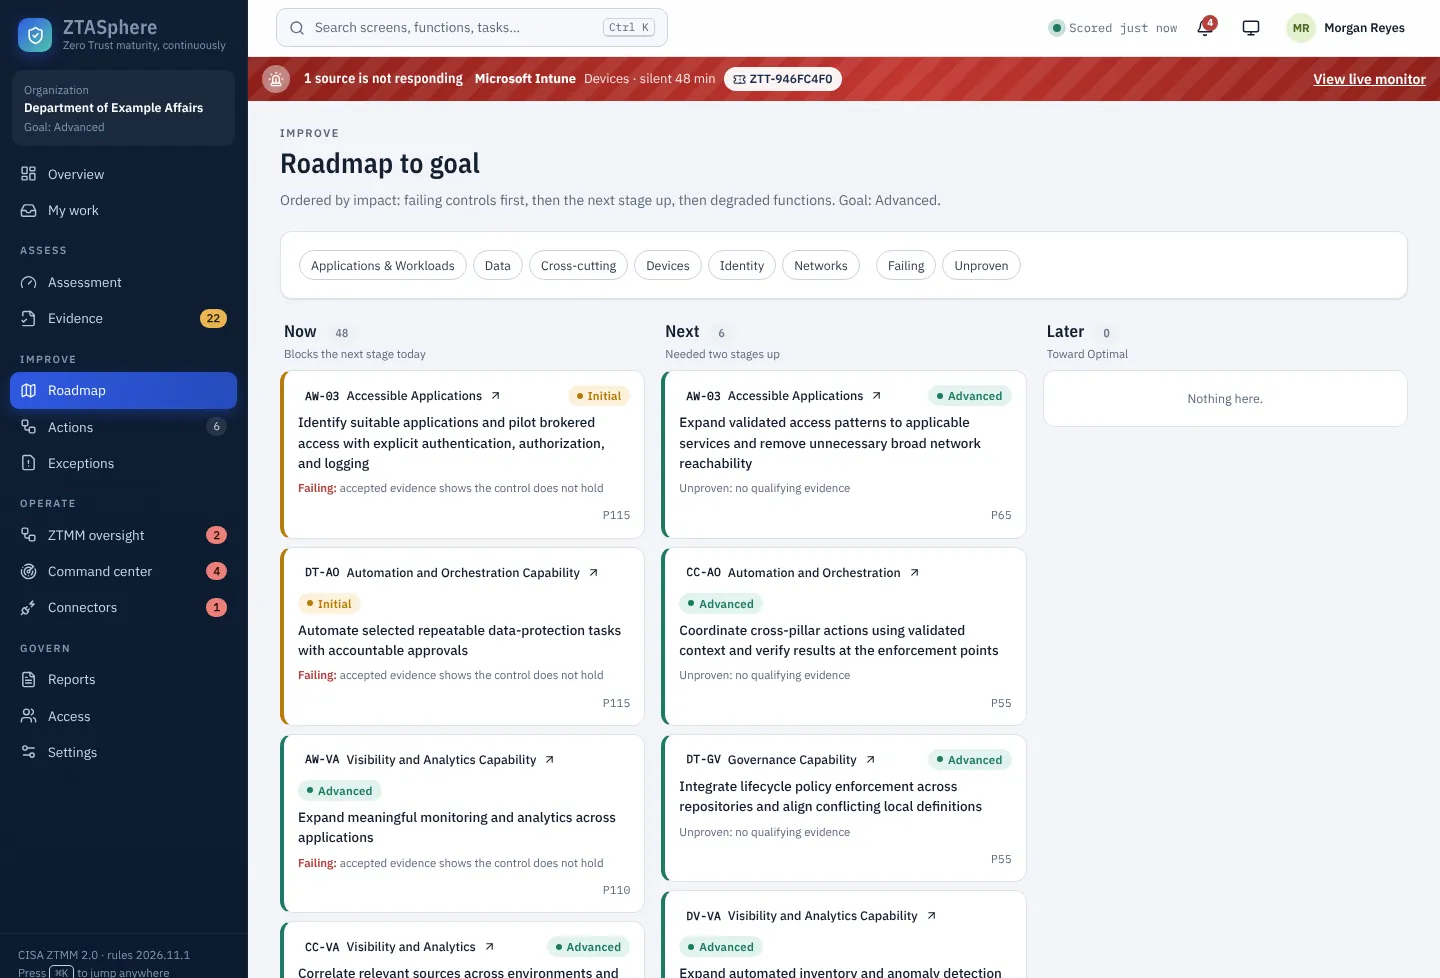
A roadmap ordered by what moves the score.
Gaps between today and your goal are ranked into Now, Next and Later, with the failing criteria and the evidence that would close each one.
- Gap-to-goal by function
- One click from gap to improvement action
- Progress verified, not self-reported
Two new memos. One place to prove progress.
OMB M-26-14 rewrote federal logging and M-26-15 started the move to post-quantum cryptography. Both come down to evidence you can show.
Logging and network visibility
Replaces M-21-31 with a five-level maturity model where the weakest component sets your level. ZTASphere tracks source inventory, coverage and feed health as evidence.
What M-26-14 requires OMB M-26-15 · June 2026Post-quantum readiness
Inventory quantum-vulnerable cryptography, prioritize high-value assets and track migration. ZTASphere probes endpoints and scores encryption maturity.
Post-quantum readinessScored on the model your auditors already use.
CISA ZTMM 2.0 defines five pillars (Identity, Devices, Networks, Applications and Workloads, Data), three cross-cutting capabilities, and four stages. ZTASphere implements the full catalog.
Manual and static
Policies set by hand, siloed tools, and maturity known only at audit time.
Starting to automate
Some cross-pillar visibility and the first automated attribute checks.
Centralized and coordinated
Automated controls, shared context across pillars, and response on risk.
Fully automated and dynamic
Just-in-time access, continuous monitoring and self-adjusting policy.
One source of truth, a different answer for each seat.
CISO
Report maturity per pillar with evidence behind every number, see which investments move the score, and catch control drift before the auditor does.
CIO
Turn EO 14028 and OMB M-22-09 goals into a funded, sequenced roadmap, and show progress in a format leadership and oversight bodies accept.
Authorizing official
Approve actions and risk exceptions with expiry dates, release reports, and rely on an audit trail that proves nobody edited history.
SOC and IR
Get alerted when a feed goes silent or a level drops, with tickets opened in the tools you already work in.
Assessors and auditors
Review evidence with SHA-256 integrity checks, verify the hash-chained audit log in one click, and export assessor-ready packages.
Return staff time to security work.
From the ZTASphere 2.0 business case, expected scenario. Counts only staff time the platform removes; risk reduction and tool rationalization are excluded.
Estimate Planning figures from an editable cost-benefit model at a $165/hour loaded labor rate. Your results depend on scope, tool count and labor rates. Run the calculator.
Engineered to the standards you assess others against.
See your zero trust maturity, scored on live evidence.
Bring one pillar or all five. In a working session we connect to the tools you already run and show what ZTASphere sees, using your own environment's language and priorities.