A system of record for zero trust maturity.
Collect evidence, score it, plan the work, govern the changes and prove the result. Fourteen screens across four jobs, one tamper-evident record underneath.
Scores you can defend, line by line.
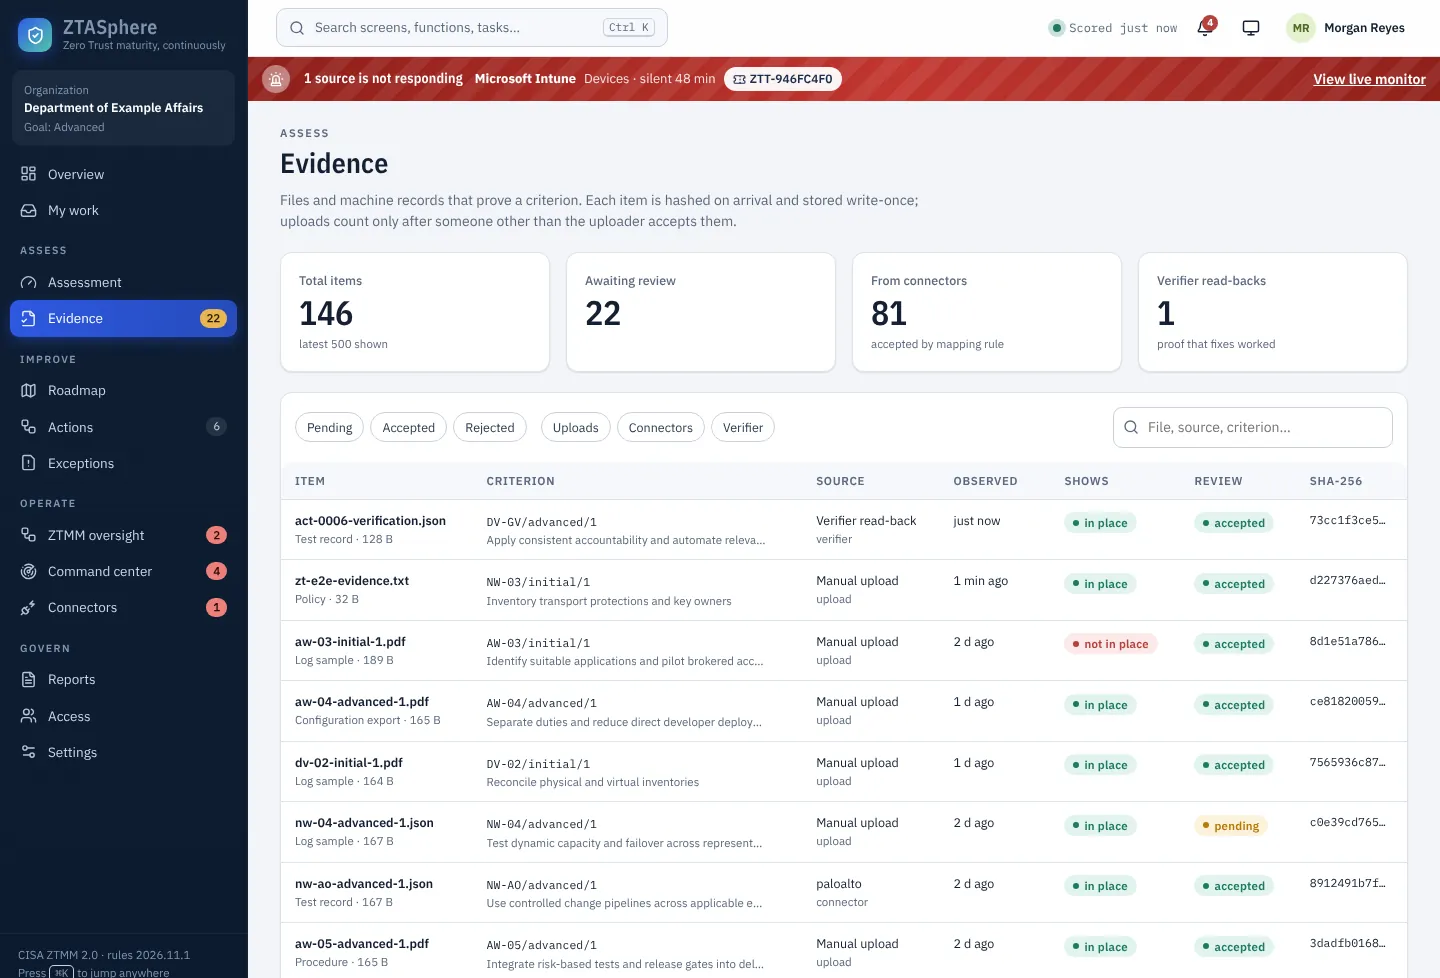
Evidence arrives from connectors or uploads, is hashed with SHA-256 on arrival and verified again on download, and is reviewed by someone other than the person who submitted it. Only accepted evidence observed within 30 days counts toward a score.
- Read-only collection through least-privilege service accounts
- Reviewer separation: uploaders cannot accept their own evidence
- Evidence requests routed to the owner who holds it
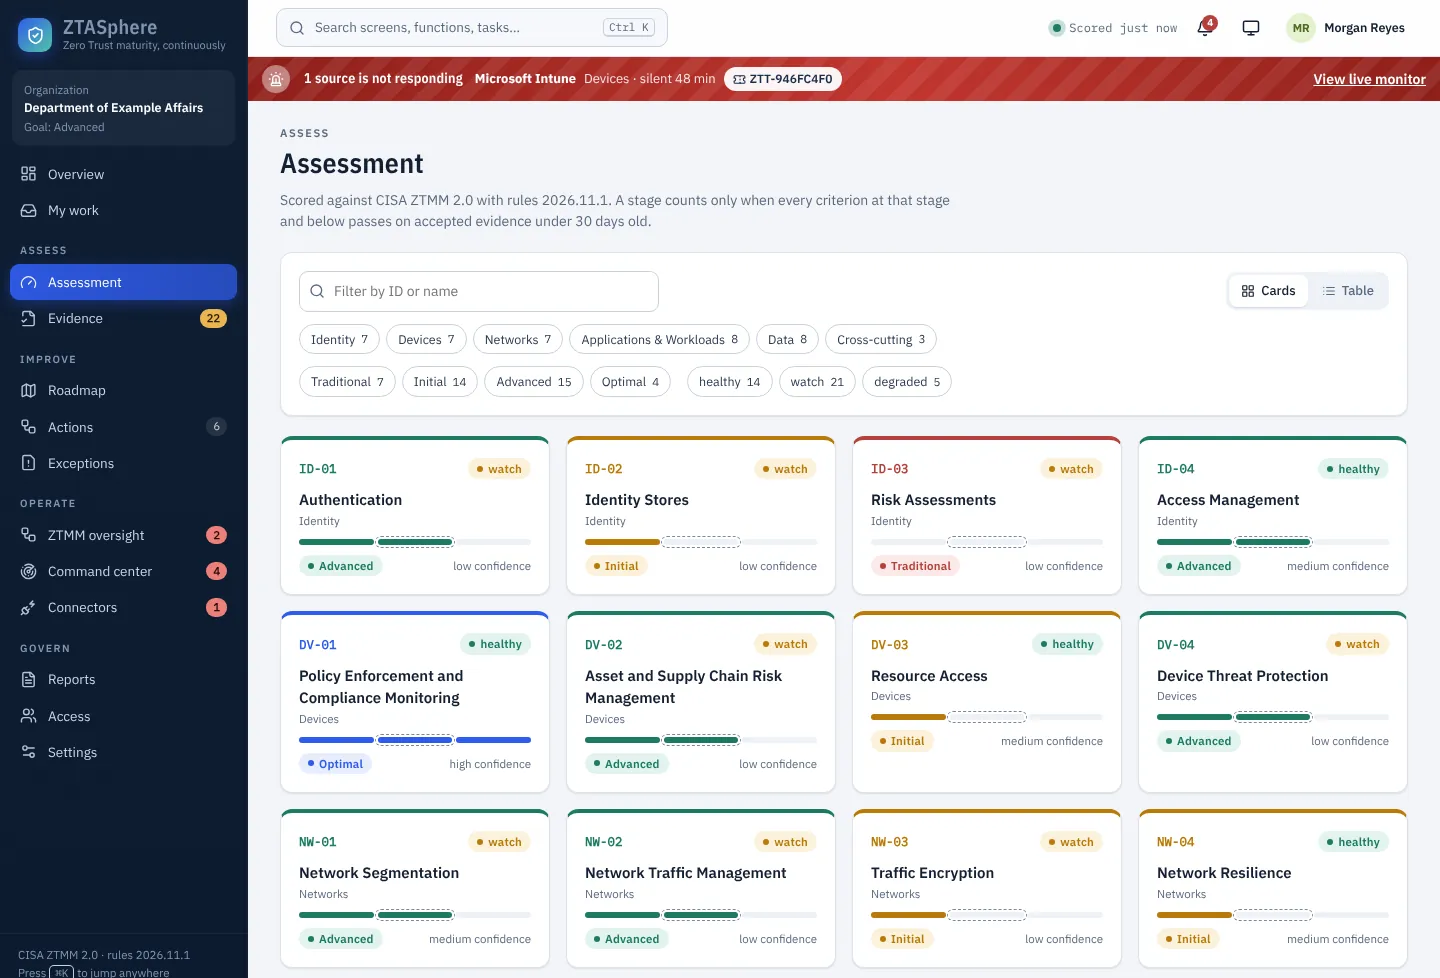
All 40 functions. All 182 criteria.
The engine evaluates every ZTMM 2.0 function against atomic criteria with versioned rules, so the same evidence always produces the same score. A stage counts only when every criterion for it is met, and each result carries a confidence level.
- Pillar × function heat map with drill-down to criteria
- Target stage per organization with gap-to-goal view
- Re-scored continuously as new evidence lands
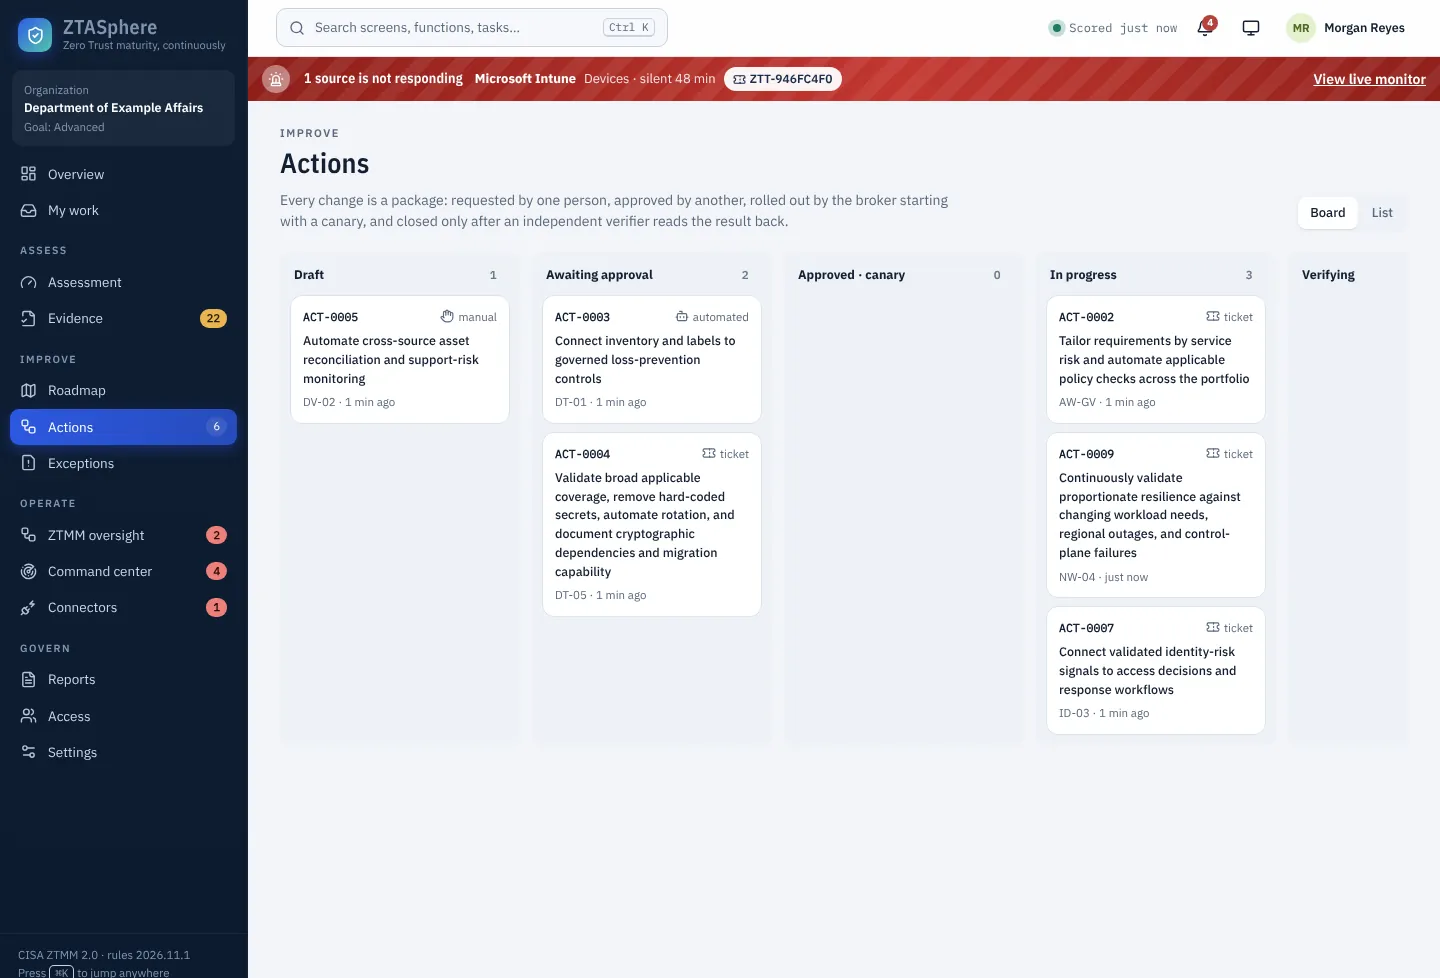
Improvement actions with real separation of duties.
Every action moves through a controlled lifecycle. The person who proposes a change can't approve it, and the result is verified by an independent reviewer with fresh evidence.
- Risk exceptions with an approver and an expiry date
- Just-in-time elevation instead of standing privilege
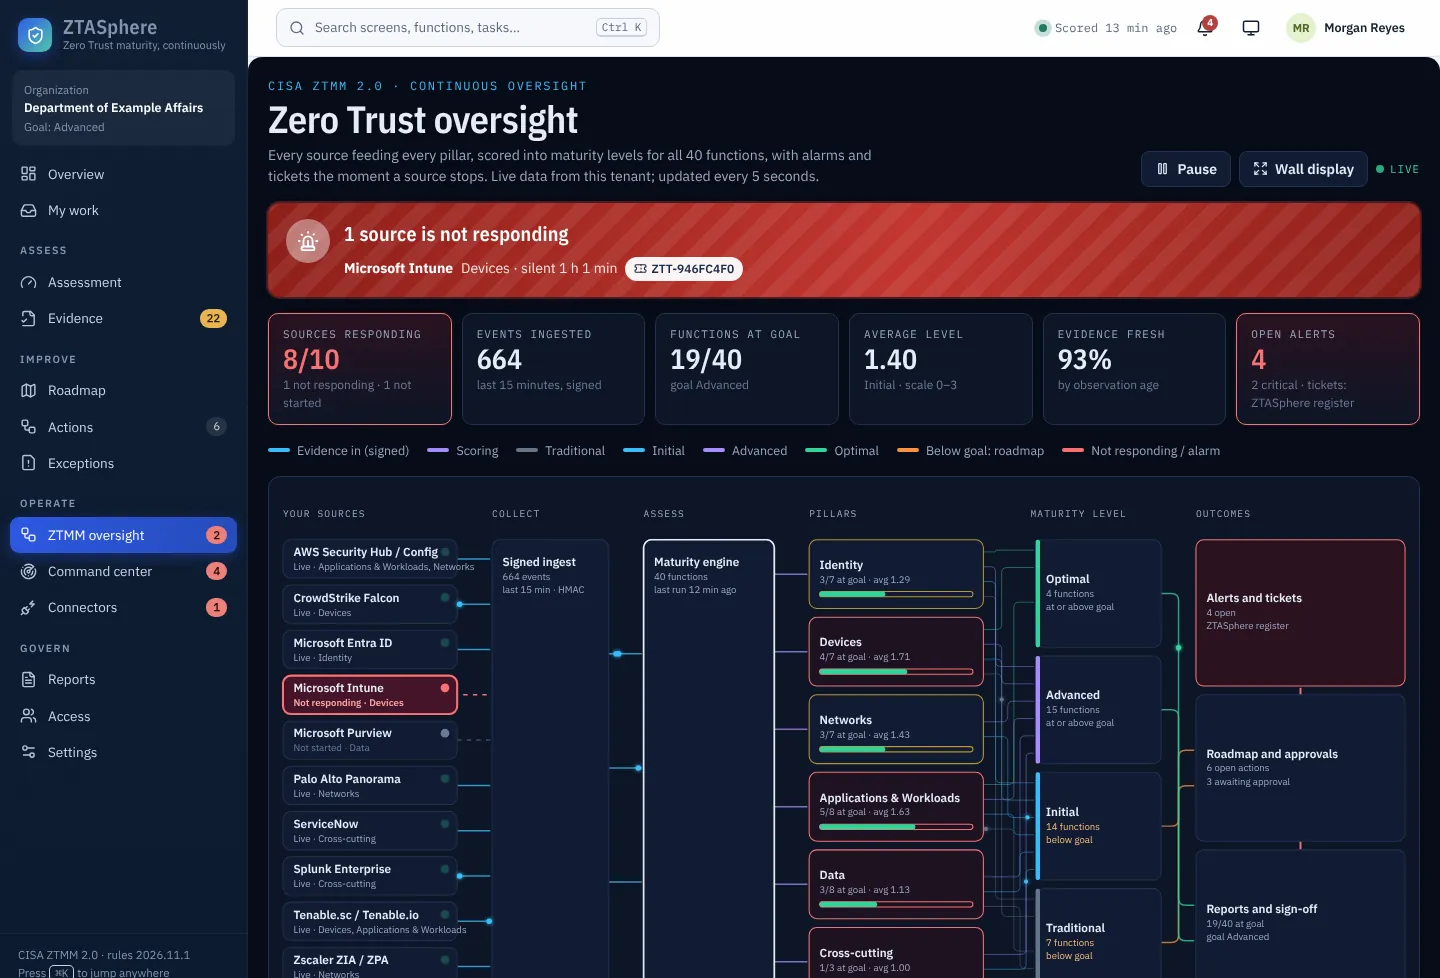
Feeds that go quiet get noticed.
Every source has a health state of live, late, down or blocked. ZTASphere escalates silence, opens tickets in ServiceNow, Jira or a signed webhook, and closes them automatically when data returns.
- ZTMM oversight wall display for the SOC
- Alarm strip on every screen when a source is down
- Drift alerts when a maturity level drops
Fourteen screens, grouped by the job to be done.
Assess
- OverviewWhere you stand against your goal and what changed
- My workReviews, approvals and verifications waiting on you
- AssessmentPillar × function heat map down to criteria
- EvidenceUpload, review and trace, SHA-256 verified
Improve
- ExceptionsRisk-accepted gaps with expiry and approver
- RoadmapGap-to-goal plan by function
- ActionsDraft to verify, with canary step
Operate
- ZTMM oversightSource-to-stage flow, alarms, wall display
- Command centerConnector health, event stream, alerts
- ConnectorsGuided add, test and silence
Govern
- ReportsExecutive, pillar, gap and CDM; draft to release
- AuditHash-chained log, one-click chain verification
- Access17 roles and just-in-time elevation
- SettingsOrganization, goal stage, banner, theme
Three independent tiers. Deploy where your mission runs.
A React web tier, a PHP 8.3 API and worker, and a MySQL 8.4 database, each built, versioned and released on its own. Ship only the modules you need without a rebuild.
Cloud
Terraform for AWS and AWS GovCloud, Azure and Azure Government, and Google Cloud. Helm overlays for EKS, AKS, GKE and vSphere Kubernetes.
On premises
A VMware appliance built with Packer and hardened with Ansible, or Docker Compose on a single physical or virtual server.
Disconnected
An offline install bundle for air-gapped networks, with signed images and a software bill of materials for every release.
See your zero trust maturity, scored on live evidence.
Bring one pillar or all five. In a working session we connect to the tools you already run and show what ZTASphere sees, using your own environment's language and priorities.